ISO/IEC 27001:2022 certification of AENIX s.r.o.

Open-source Cozystack (a CNCF project we create and maintain) → Ænix Platform, the supported commercial distribution → Aenix builds, operates and migrates it.

AENIX s.r.o., the Czech company behind the Ænix platforms and the maintainers of Cozystack, holds an ISO/IEC 27001:2022 certificate for its information security management system (certificate № SIC.MS.008.ISO/IEC27001.5719, issued 27 February 2026). The certificate covers software development, IT consulting, hosting, data services and web portals. It certifies how the company manages information security — policies, risk treatment, incident handling, access, suppliers, internal audit — not a software product: Cozystack and the platforms built on it are not “ISO 27001 certified” products, and a customer’s own environment needs its own certification. Validity runs to 26 February 2027, renewed through annual surveillance audits within a three-year cycle ending 26 February 2029.

Quick facts

  • Certified organisation AENIX s.r.o., U Trojice 2661/1E, České Budějovice, Czech Republic.
  • Standard ISO/IEC 27001:2022 — information security management systems, requirements.
  • Certificate number SIC.MS.008.ISO/IEC27001.5719
  • Scope Software development, IT consulting, hosting, data services, web portals.
  • Validity Issued 27 February 2026; valid through 26 February 2027; next surveillance audit 27 January 2027; certification cycle to 26 February 2029.
  • Certification body Bureau of International Certification (Kyiv), part of the System of International Certification (SIC); accreditation GAS.CB.804.008, Global Accreditation System (GAS), 11 January 2025.
  • Not covered AENIX INC (US), customer deployments of the platforms, and the software itself as a product.

Source: Certificate № SIC.MS.008.ISO/IEC27001.5719 and the AENIX s.r.o. ISMS documentation, approved 17 February 2026.

AENIX s.r.o. holds an ISO/IEC 27001:2022 certificate for its information security management system, issued on 27 February 2026 under number SIC.MS.008.ISO/IEC27001.5719. The scope, as written on the certificate, is software development, IT consulting, hosting, data services and web portals.


The certificate
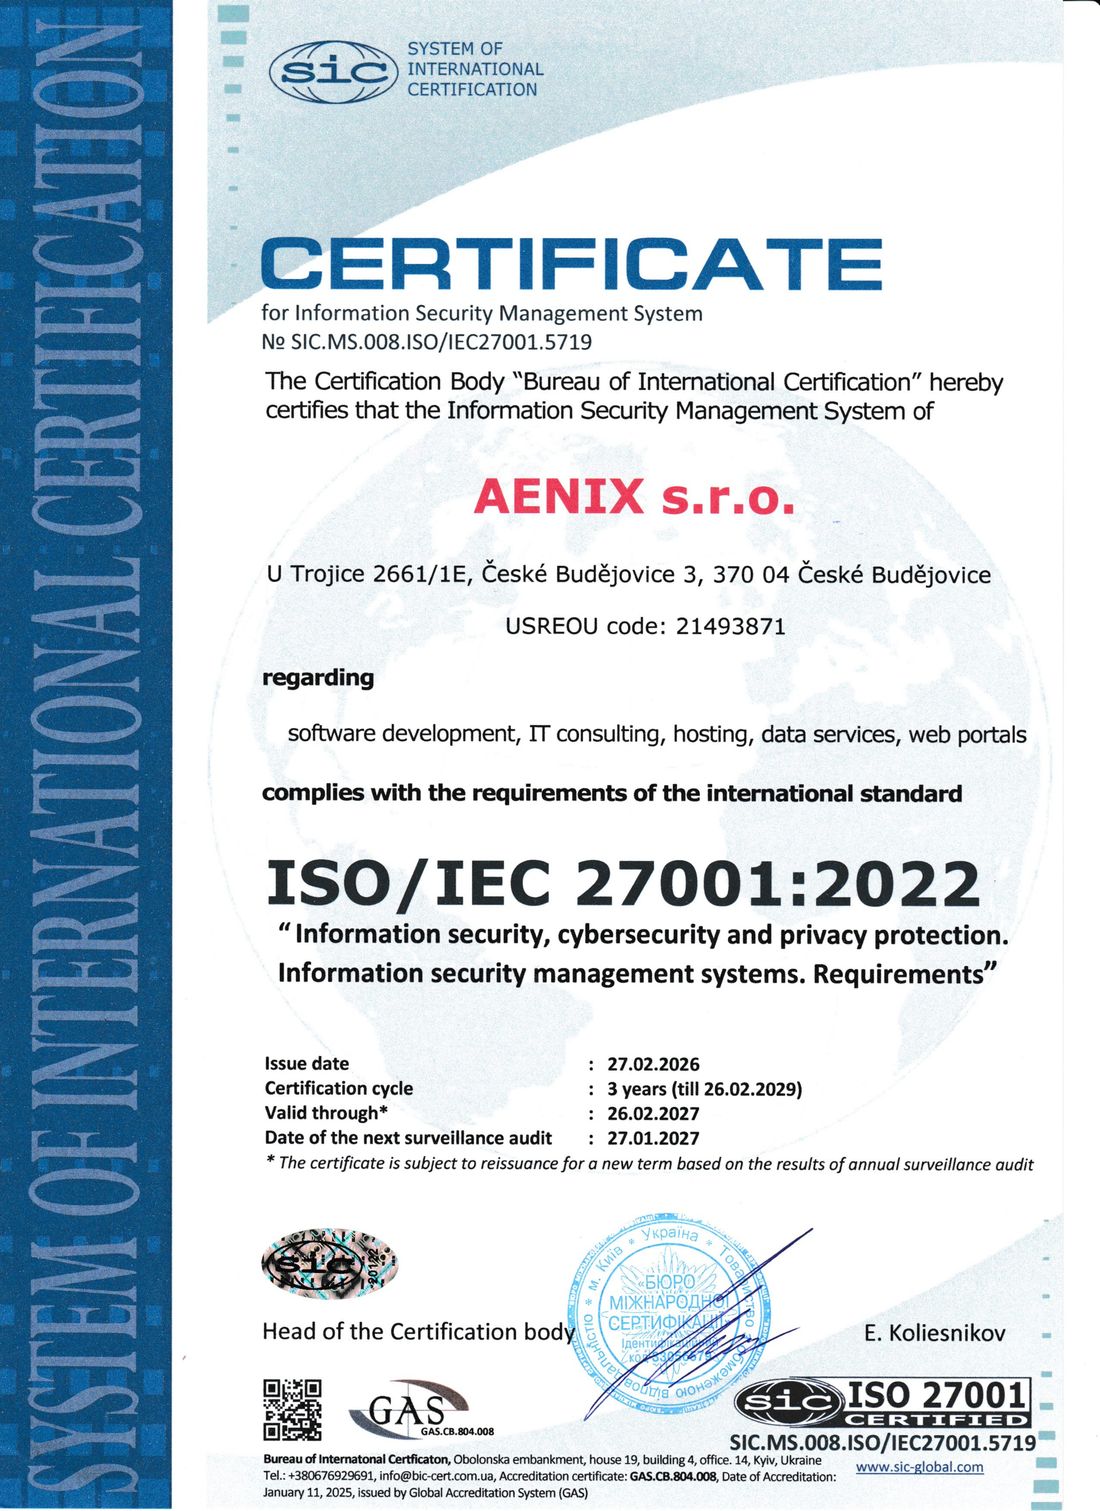
ISO/IEC 27001:2022 certificate of AENIX s.r.o., number SIC.MS.008.ISO/IEC27001.5719

Certificate № SIC.MS.008.ISO/IEC27001.5719, issued 27 February 2026, valid through 26 February 2027.

OrganisationAENIX s.r.o., U Trojice 2661/1E, České Budějovice 3, 370 04 České Budějovice, Czech Republic
StandardISO/IEC 27001:2022, Information security, cybersecurity and privacy protection — Information security management systems — Requirements
ScopeSoftware development, IT consulting, hosting, data services, web portals
Issued27 February 2026
Valid through26 February 2027, renewed on the results of the annual surveillance audit
Next surveillance audit27 January 2027
Certification cycleThree years, to 26 February 2029
Certification bodyBureau of International Certification, Kyiv; System of International Certification (SIC)
Accreditation of the bodyGAS.CB.804.008, Global Accreditation System (GAS), 11 January 2025

What the certificate means, and what it does not

ISO/IEC 27001 certifies a management system, not a product. It says that AENIX s.r.o. runs information security as a managed process: risks are assessed and treated, controls from Annex A are selected and justified, incidents are handled by procedure, access is granted and reviewed by procedure, and the whole system is audited internally and by the certification body.

It does not make Cozystack or the Ænix platforms “certified software”, and it does not certify your environment. If you build a regulated service on the platforms, your own scope, risks and controls are yours to manage and, if you need a certificate, yours to certify. What the platforms contribute to that work — tenant isolation, audit logging, access control, encryption, declarative change control — is mapped control by control on the PCI DSS, GDPR, DORA and CIS Benchmark pages.

The certificate is held by AENIX s.r.o., the Czech company. AENIX INC, the US company, is not named on it.

The ISMS behind it

The documented information security management system of AENIX s.r.o. was approved by the CEO, Andrei Kvapil, on 17 February 2026. It includes:

  • an information security policy and an instruction on complying with it;
  • policies for information asset management, physical security, information security incident management, clean desk and clear screen, and user identification management;
  • procedures for information classification, management of documented information, and internal audit;
  • measurable ISMS objectives with the actions planned to reach them.

Customers and prospects can receive copies of the policies under NDA, together with the signed certificate.

Verifying the certificate

The certificate carries a QR code and its number, SIC.MS.008.ISO/IEC27001.5719. Both can be checked with the certification body through the System of International Certification at sic-global.com. If your procurement process needs the signed PDF or a confirmation letter, ask us through the contact page.

Frequently asked questions

Is Ænix ISO 27001 certified?

AENIX s.r.o. is. Its information security management system is certified to ISO/IEC 27001:2022, certificate № SIC.MS.008.ISO/IEC27001.5719, issued 27 February 2026 and valid through 26 February 2027 with annual surveillance audits. The certificate is held by the Czech company; AENIX INC in the United States is not named on it.

Does the certificate make the Ænix platforms or Cozystack certified?

No. ISO/IEC 27001 certifies an organisation’s management system, not a product. What the certificate tells you is how AENIX s.r.o. develops, supports and hosts — how it handles risk, access, incidents, suppliers and changes. Your own environment built on the platforms needs its own ISMS and, if you want one, its own certificate; the platforms supply technical controls that make that work easier, described on the other compliance pages.

What does the scope cover?

As written on the certificate: software development, IT consulting, hosting, data services and web portals. This is the work AENIX s.r.o. does for customers, including the development of Cozystack and the Ænix platforms and consulting engagements.

Which policies does the ISMS include?

Among others: an information security policy, information asset management, physical security, information security incident management, clean desk and clear screen, user identification management, information classification, management of documented information and an internal audit procedure, plus measurable ISMS objectives. They were approved by the CEO on 17 February 2026. Copies are available to customers under NDA.

How can we verify the certificate?

The certificate carries a QR code and its number, SIC.MS.008.ISO/IEC27001.5719, which can be checked with the certification body through the System of International Certification (sic-global.com). We can also send the signed certificate PDF directly; ask through the contact page.

Do you also have SOC 2?

No. There is no SOC 2 report for Ænix. Where a customer needs SOC 2 for their own service on the platform, the platform supplies control evidence; the report is theirs.